October 2026 | IT Support for Manufacturers Salt Lake City | Security Culture | Plant-Wide Awareness
It's 4:17 on a Friday afternoon at a Salt Lake City manufacturing company. The last production run of the week is winding down, and the front office is trying to close out before the weekend.
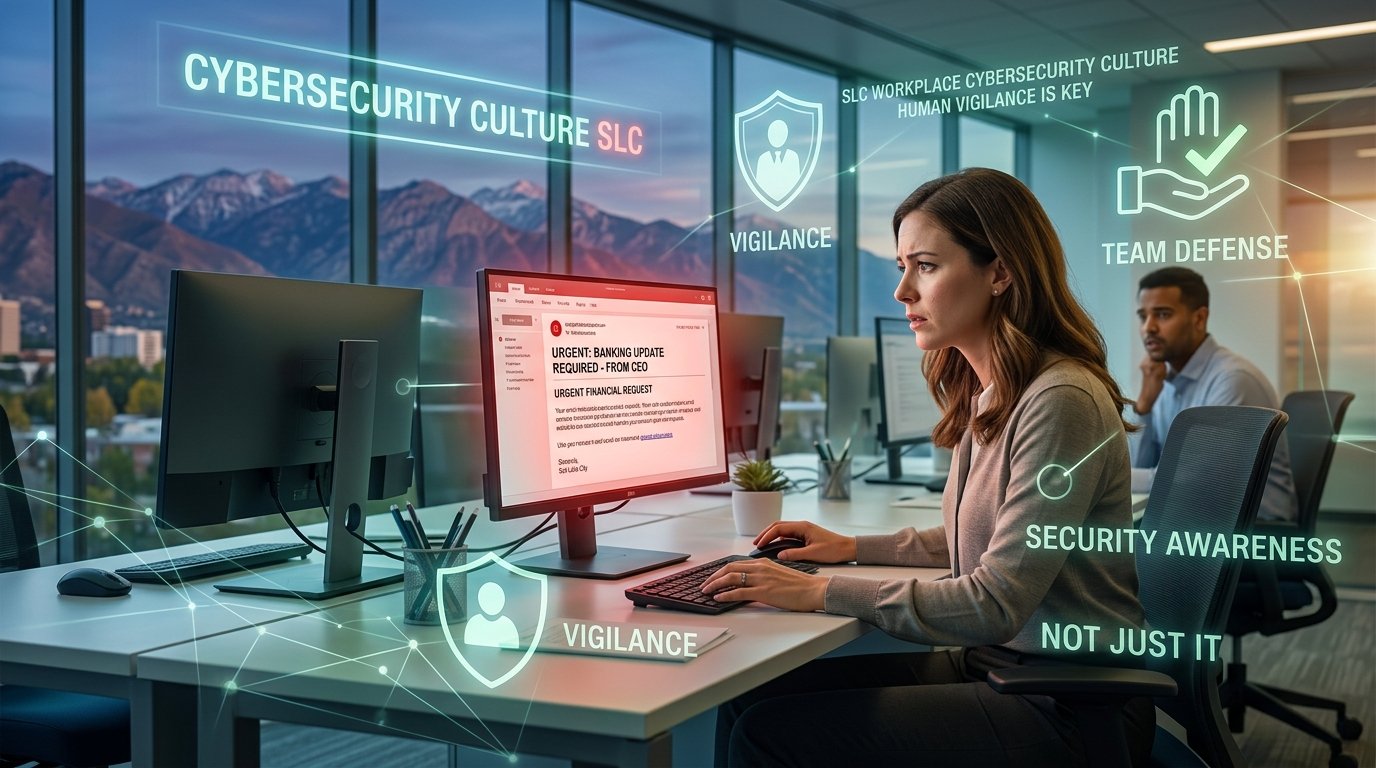
Someone in accounting receives an email that appears to be from the owner: "Can you update the banking details for our steel supplier before you leave? They need it processed before Monday's shipment."
The name is right. The tone sounds familiar. The supplier is real. And with everyone trying to wrap up the week, the easiest thing to do is simply make the change. There's only one problem: the owner never sent it.
Your security tools can put strong protections in place, but they can't stop every bad click, rushed reply or split-second payment change. Some decisions still come down to whether an employee — in the office or on the floor — knows what to do when something feels off.
The Assumption That Leaves Manufacturers Exposed
Most owners and plant managers believe cybersecurity lives somewhere behind the scenes. The IT team has tools. The computers have protection. Someone schedules the updates on the ERP server. Cybersecurity is "handled."
In reality, your defenses are tested every time someone decides whether to trust an email, link or request — the purchasing manager approving a PO in Epicor, the engineer opening a "revised drawing" attachment, the supervisor logging into a shared terminal on the floor. Those decisions happen every day, across every part of your operation. To truly strengthen your security, your production and operations team must know what to do when something doesn't look right.
Technology Can't Make Every Call
Good security tools block a lot of attack attempts before employees ever see them. But no technology can eliminate every questionable request or make every decision on an employee's behalf.
Today's phishing attacks aren't obvious. They're built to mimic familiar writing styles, reference the suppliers and freight carriers you actually use and mirror the rhythm of normal purchasing conversations. When an unusual payment request comes from the owner, a supplier legitimately changes banking details mid-contract, or a machine vendor asks for remote access to "push an urgent update" — someone must decide what happens next. The employee at the keyboard has to determine, in an instant, whether they're looking at a scam or an authentic request.
Get that call wrong on an invoice, and you lose money. Get it wrong on a vendor remote-access request, and an attacker is one hop away from the systems running your line.
"Be Careful" Isn't a Cybersecurity Plan
Most manufacturers tell employees to watch out for suspicious emails. But what should they actually do when they find one? Everyone — front office and shop floor alike — should know:
- Who to contact, whether they sit in accounting or run a CNC machine
- How to verify a request is legitimate — a call-back to a known number, every time payment details change
- Not to click links or download attachments from suspicious messages, including fake POs and "updated drawings"
- What to do if they already clicked a link or opened an attachment
- How to report the issue quickly, without paperwork or blame
Telling everyone to simply "be careful" without a clear next step puts the full weight of a high-stakes decision on the person least equipped to handle it in the moment — often someone whose job is running production, not spotting fraud.
Assuming employees know what to do is a liability. An operator who isn't sure whether they're bothering someone may stay quiet. An office employee who fears getting blamed for clicking the wrong thing may wait before reporting it. Hesitation is costly — the time lost while someone decides whether to speak up can turn a contained incident into a full production shutdown.
Leadership Sets the Tone
Responsibility starts at the top, because employees take their cues from leadership. If the owner routinely skips verification steps because a shipment is on the line, employees learn that speed matters more than process. If the plant manager makes it uncomfortable to flag suspicious activity, the floor stays quiet. If someone clicks something they shouldn't and gets publicly reprimanded in the break room, everyone learns to hide their mistakes.
Fortunately, the opposite is also true. When leadership normalizes verification — even under delivery pressure — employees take it seriously. When an employee who questions an unusual request is backed up rather than brushed off, the whole operation runs more carefully. When your production and operations team trusts leadership, they speak up before a situation becomes a crisis that stops the line.
Cybersecurity Works Better When Everyone Knows Their Role
Back to that accounting employee at 4:17 on a Friday afternoon.
The goal isn't to make your people paranoid about every email. It's to make sure that when something feels off, they know exactly what to do, who to ask and how to verify. Speaking up should always feel like the right move — because the alternative is explaining to customers why their orders are late.
Your employees don't need to become cybersecurity experts to help protect the business. They need clear expectations, good habits and the confidence to flag when something doesn't look right — whether that's a strange invoice, a login prompt that looks slightly wrong or a vendor connection nobody scheduled.
Creating that kind of security culture takes more than an annual training session. It requires the right safeguards, practical verification processes and ongoing guidance that keeps pace as threats change — the kind of support the right manufacturing IT services partner provides.
Frequently Asked Questions
Do you offer IT and cybersecurity support for manufacturing companies in Salt Lake City?
Yes. Qual IT delivers IT support for manufacturers in Salt Lake City and across the Wasatch Front, including email security, phishing protection, verification process design, security awareness training for both office and shop floor staff, OT vendor access management and incident response planning.
What is security awareness training for manufacturing employees?
It's structured, ongoing education that teaches your production and operations team to recognize phishing, fake supplier invoices and social engineering — and gives them a clear process for verifying and reporting suspicious activity. Done well, it turns your whole workforce into an active layer of defense instead of the gap in it.
How does an IT partner help build a security culture in a plant?
A partner like Qual IT identifies your gaps, implements the right safeguards across IT and OT, sets up practical verification and reporting processes that work under production pressure, and provides the ongoing training that keeps security habits current as threats evolve.
You Don't Have to Manage It Alone
We work with Salt Lake City manufacturers to protect production systems and reduce operational downtime. Qual IT helps take the guesswork out of industrial cybersecurity by identifying gaps, strengthening protections and helping every employee — from the front office to the shop floor — understand the role they play in keeping the business running.
Cybersecurity is everyone's responsibility — but you don't have to manage it alone. Schedule a 10-minute discovery call with Qual IT to find the gaps in your current approach and how to close them. Book your discovery call here.